
Cybersecurity Graduate & Malware Analyst Dedicated Cybersecurity professional with a Bachelor’s degree and specialized expertise in Malware Analysis and SOC Operations. I possess a deep understanding of the end-to-end security operations lifecycle, from proactive threat hunting to real-time incident response. My technical background is distinguished by advanced work in Mobile Security and Applied AI, where I have successfully integrated Machine Learning modeling including feature engineering and behavioral classification to detect sophisticated Android-based threats. I am passionate about bridging the gap between traditional security analysis and automated, intelligence-driven defense systems.
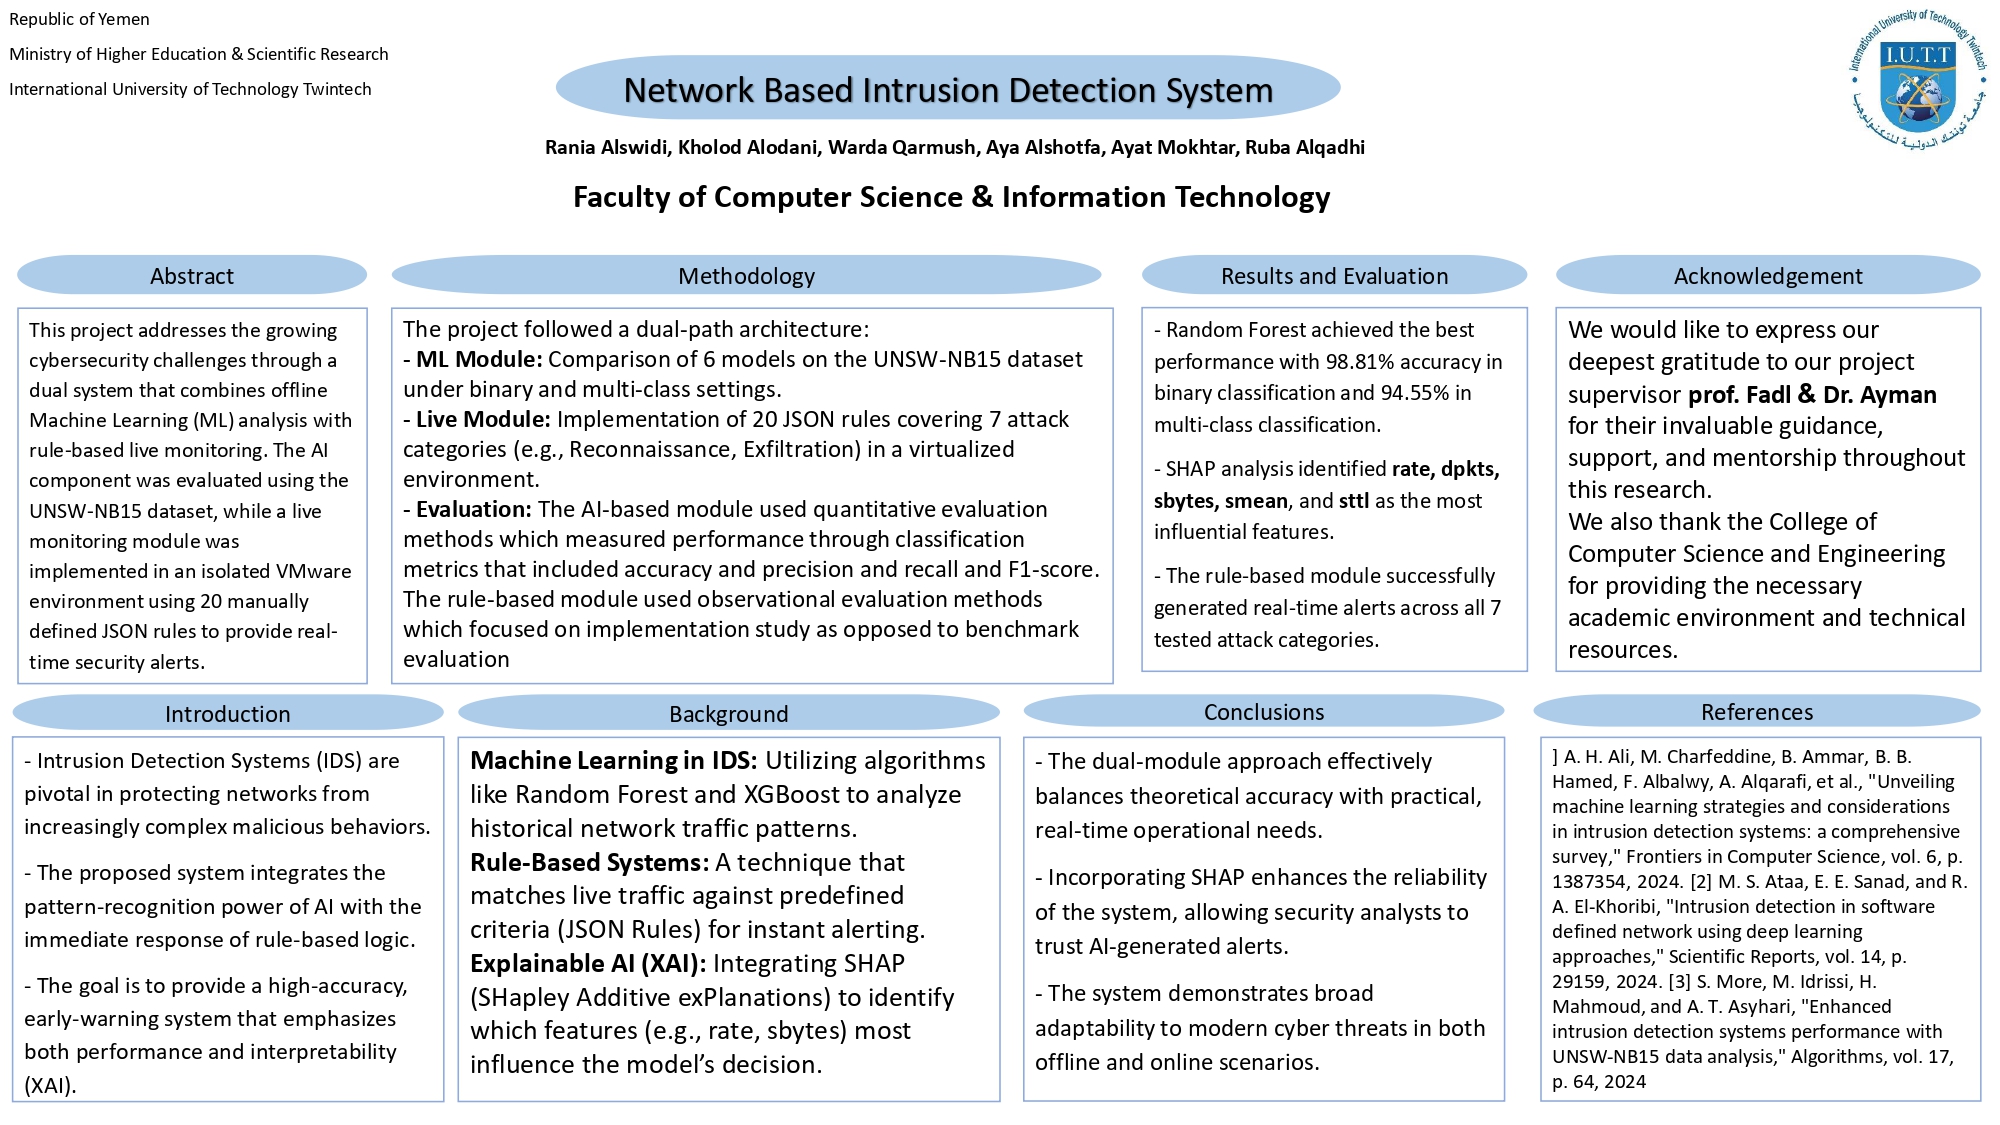
The project focuses on detecting network-based intrusions by building an intelligent model capable of detecting attacks and suspicious activities, along with analyzing the most important features that play a key role in identifying intrusion attempts, thereby enhancing detection efficiency and the accuracy of security decision-making.
I am passionate about understanding how the web works and how to secure it. My main interest is web security — exploring vulnerabilities, studying attack methods, and learning defense strategies to build safer systems.
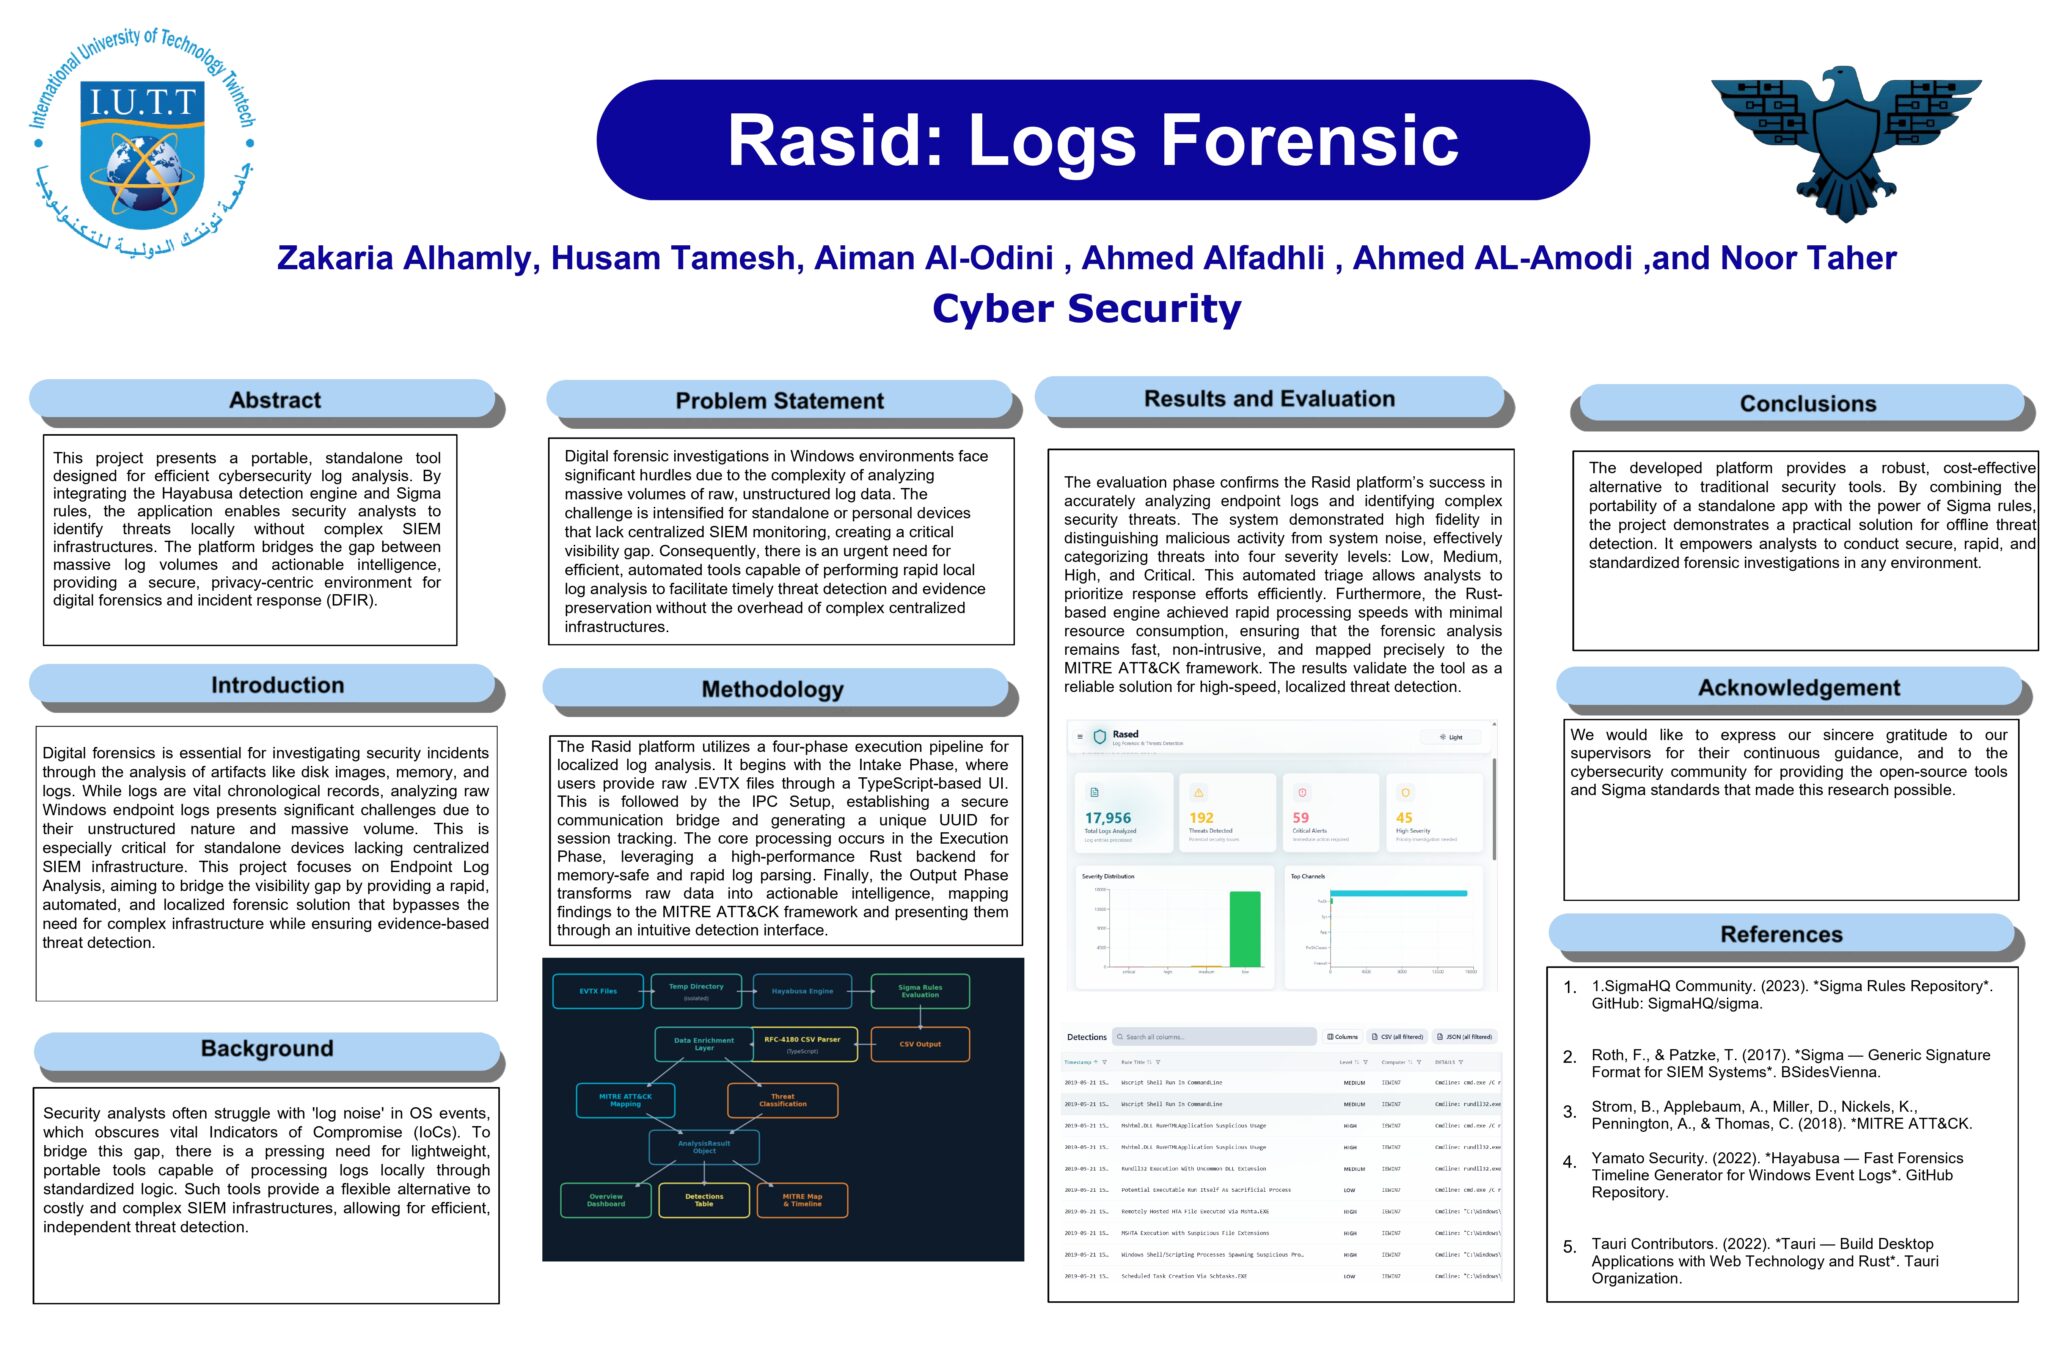
This project presents a portable, standalone tooldesigned for eficient cybersecurity log analysis. Byintegrating the detection engine and Sigmarules, the application enables security analysts toidentify threats locally without complex infrastructures. The platform bridges the gap betweenmassive log volumes and actionable intelligence,providing a secure, privacy-centric environment fordigital forensics and incident response (DFIR)
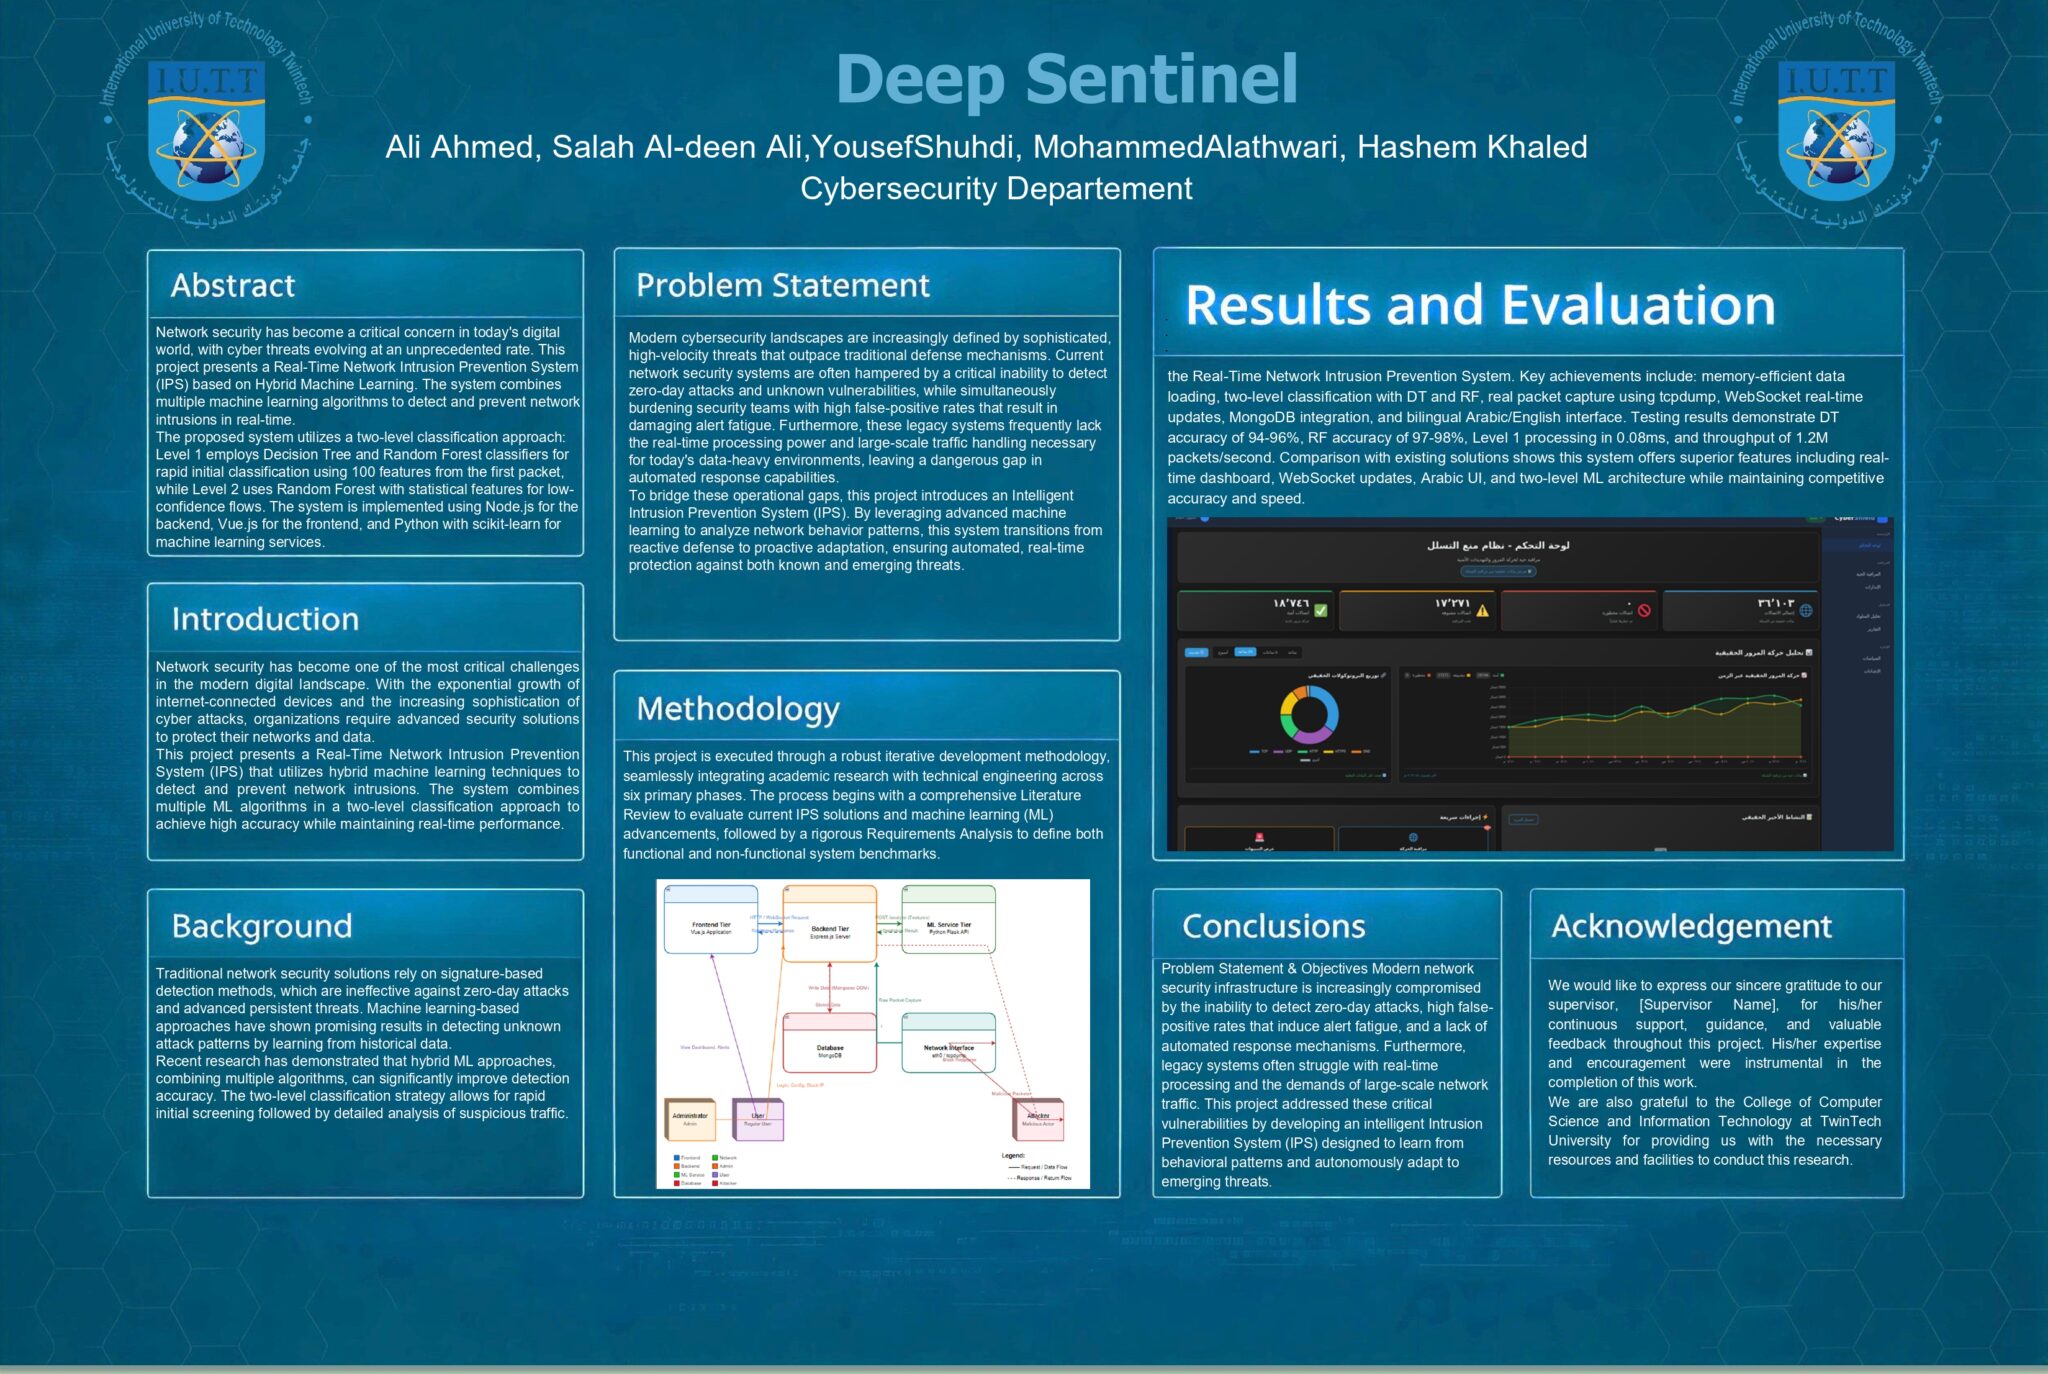
This project presents the design and implementation of a Real-Time Network Intrusion Prevention System (RT-NIPS) based on a machine learning methodology. The system addresses the fundamental challenge in network security: achieving both high detection accuracy and real-time processing speed simultaneously. The proposed system employs a two-level classifier architecture. Level 1 performs fast classification using Decision Tree (DT) on the first packet of each flow. Level 2 performs fine-grained analysis on low-confidence flows using Random Forest (RF) with full flow statistics. The system was trained and evaluated on two benchmark datasets: UNSW-NB15 and CICIDS2017. Key results demonstrate that the two-level approach successfully balances speed and accuracy.
Cybersecurity graduate from Tuntech University, Interested in the field of cloud computing security and GRC, and aiming to develop my skills and gain practical experience in this field.
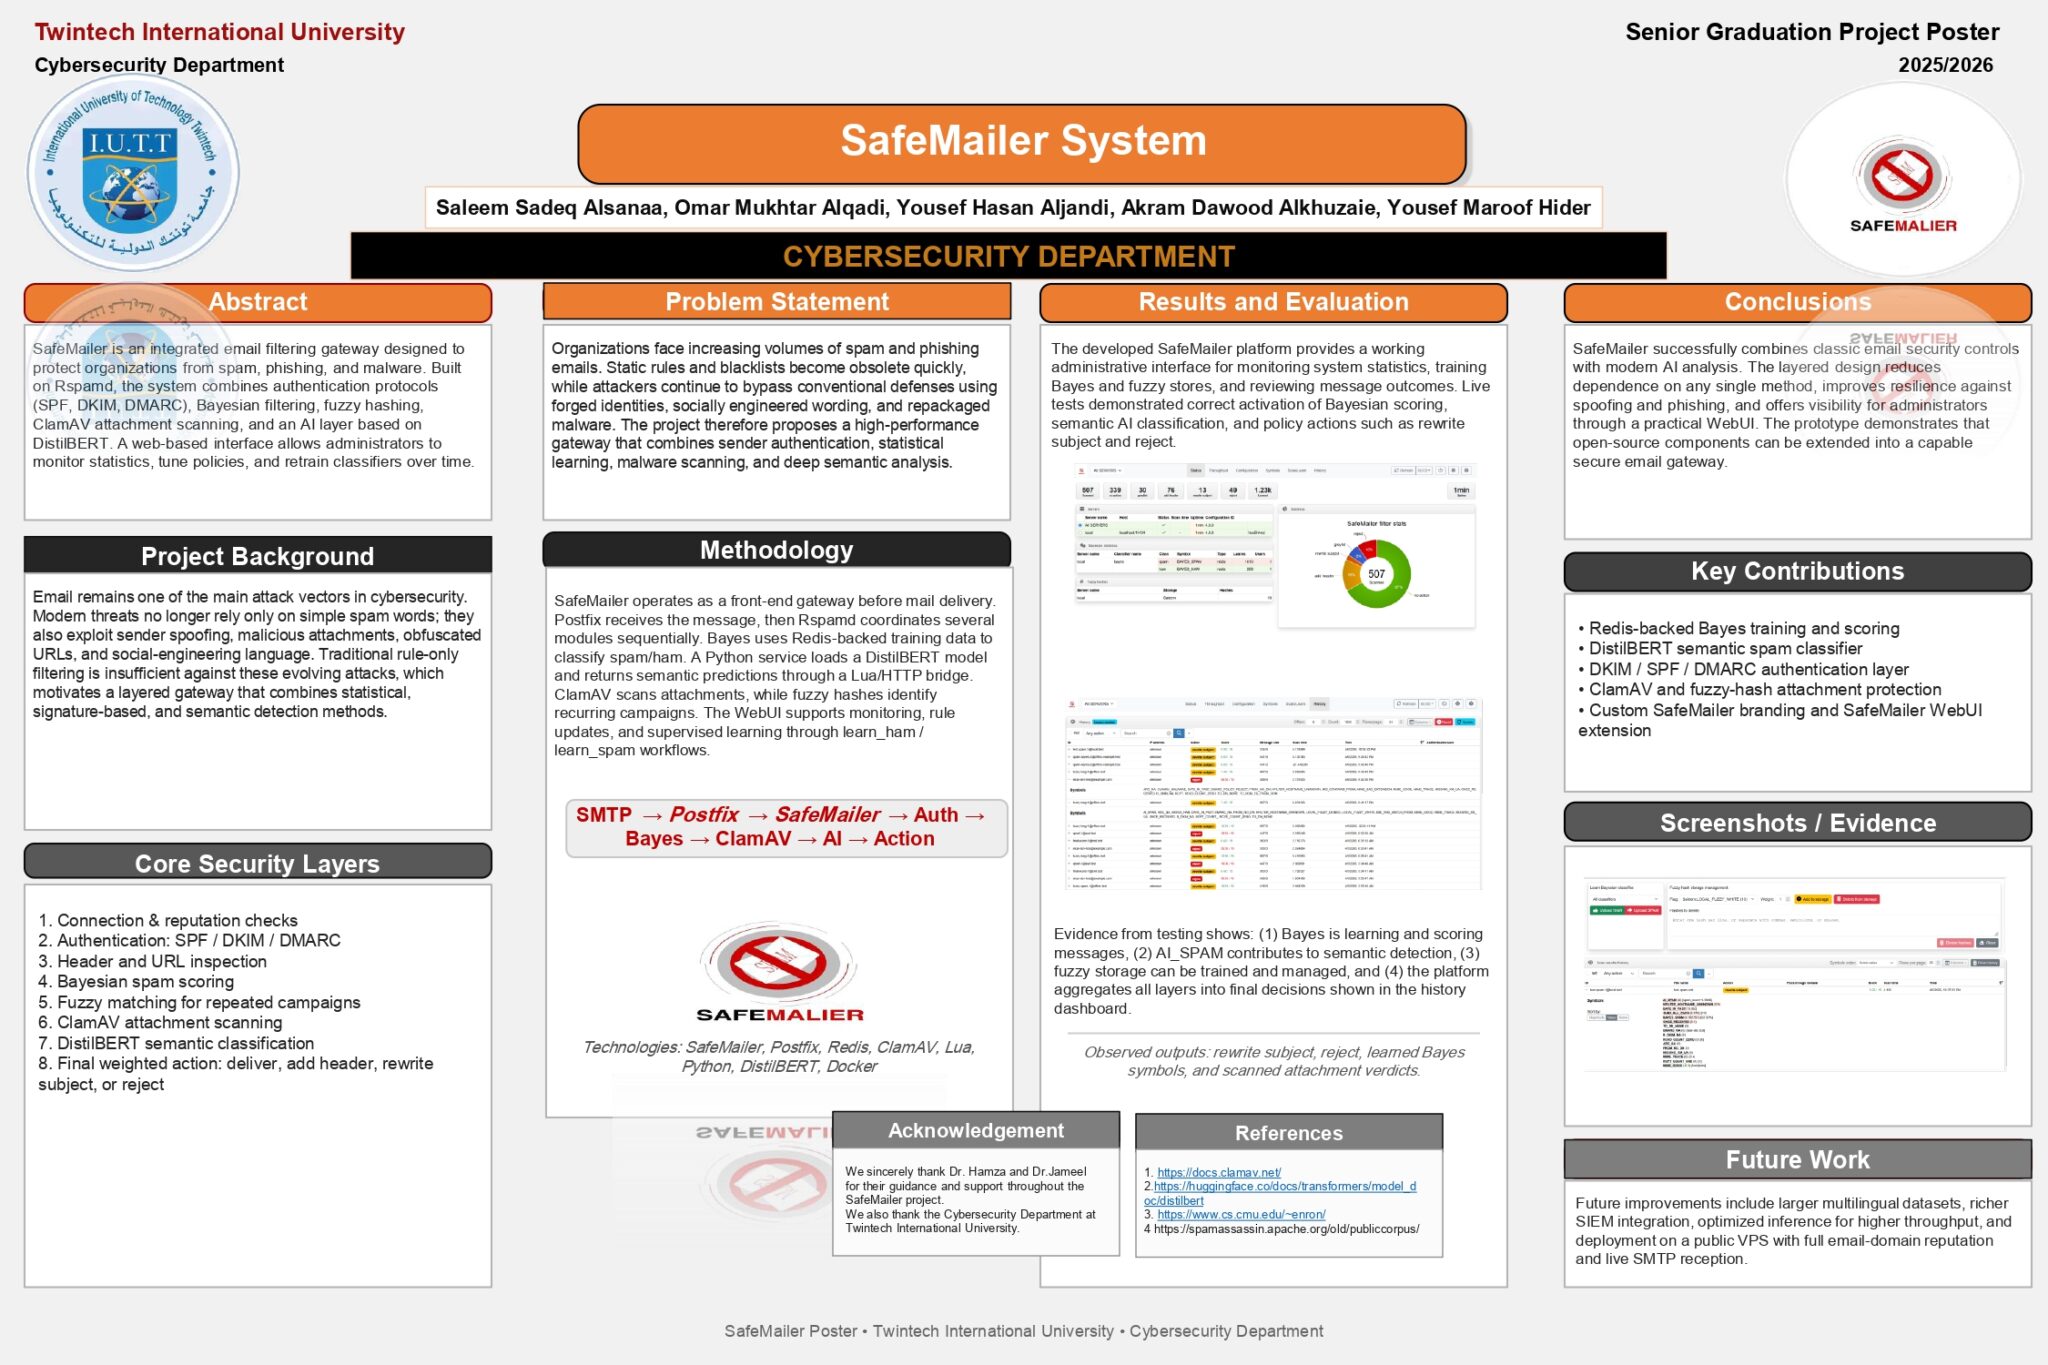
SafeMailer is an intelligent email filtering gateway designed to enhance organizational security against spam messages, phishing emails, and malicious software. The project is built on a multi-layered architecture that combines sender identity verification using SPF, DKIM, and DMARC protocols, statistical classification through the Bayes classifier, attachment scanning using ClamAV, and threat similarity detection through Fuzzy Hashing. In addition, the system employs the DistilBERT model as an artificial intelligence layer for semantic analysis of email content. The system also provides an administrative web interface for monitoring results, managing policies, and retraining classifiers, which contributes to improving detection efficiency, reducing false positives, and continuously enhancing overall system performance.